Staying ahead of cybercriminals in 2026 means treating security as a layered, converged system rather than a stack of standalone tools, because attackers already operate that way. Threat actors now combine AI-driven tactics, ransomware-as-a-service, and detailed reconnaissance to move faster than most defenses can respond, and legacy single-checkpoint security cannot keep pace.
- Cybercrime has professionalized: ransomware operators run call centers and price attacks around a target's cyber insurance limits, while crime-as-a-service lowers the skill bar for less experienced attackers.
- Detection is getting harder, not easier: for the first time in five years, the average time to identify and contain a breach increased in 2026, up 2.5% year over year (IBM Cost of a Data Breach Report 2026).
- Smaller and mid-sized organizations are now frequent targets precisely because they run the same software-defined infrastructure as larger enterprises without matching security maturity.
- The fix is layered, converged security, where identity, access, and context signals inform each other, not one more point solution bolted onto the stack.
Businesses have their backs against the wall as cybersecurity threats increase in frequency and severity. Proximia believes it's time for security teams to be as imaginative and innovative as threat actors have become. Not just new approaches to fundamentals but evaluating new kinds of defenses and controls as well. As risk slows the business down, security must move faster.
How did we get here?
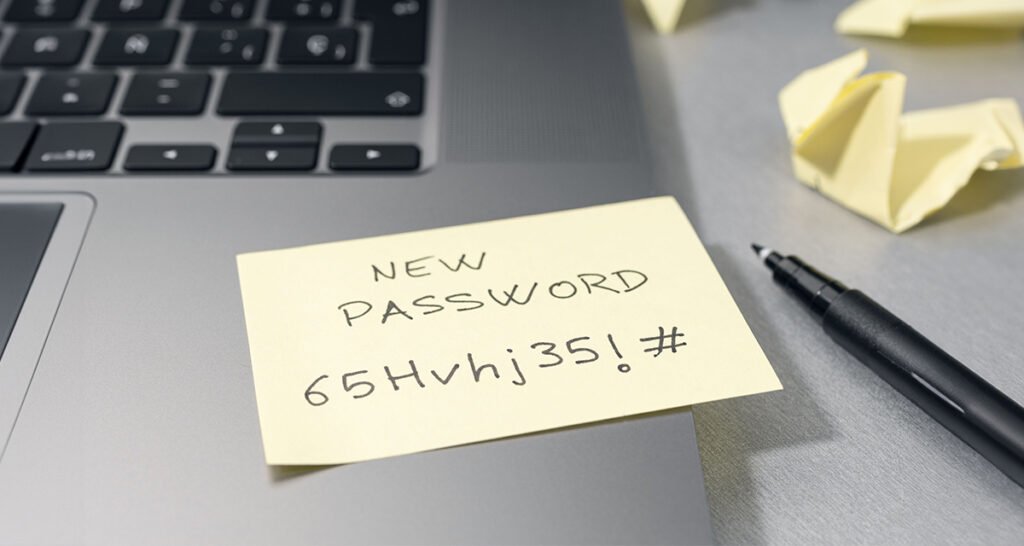
To add protection, many turn to MFA, often using bioauthenticators like Face ID. While MFA restricts unauthorized access initially, it doesn't secure the entire session. Additionally, current MFA methods can be cumbersome and time-consuming, leaving users frustrated and less likely to embrace these security measures.
In the outside world, it's easier to get good at being bad
If you've seen more than one heist movie, you know how much work goes into the setup. First, recruit the right professionals. Then it's on to selecting a target and finally all those classic stakeout and surveillance scenes. And all this takes place before the job even goes off.
Say what you want about those movie bad guys – their work ethic was typically impeccable.
While it's true that criminals have never been as smart or determined as they are in the movies, they don't have to be. The same digital changes transforming how we live and work have made it very easy for a single bad actor to have the same diverse capabilities of a well-curated Hollywood heist crew.
They're getting smarter
With all the information they can get by browsing, buying, or stealing, threat actors can quickly understand your business and identify your most valuable resource(s). For ransomware attacks, again the leading attack type, the real prize isn't data, but your ability to do business. It's like the heist crew stealing the bank itself.
Finally, they're also getting smarter about their business model. Large ransom operations even run call centers to speed the payment of demands. Some attacks are made with full knowledge of cyber insurance limits in order to drive faster payouts. It's hard not to be a little impressed.
Technology lets them do more with less
The huge financial incentives in cybercrime drive a culture of continuous innovation that most businesses would envy. This advancement enables attackers to combine and converge individual threats, tactics, and procedures into complex, multiphase threats.
This also includes threat actors using AI and GenAI to become more effective. From supercharged tactics such as automated port scanning to sophisticated Gen AI deep fakes, cybercriminals are using AI to stay ahead of your defenses. It all comes together in crime as a service, where cybercriminals offer their services to others. This creates a very dangerous marketplace where even relatively inexperienced threat actors can easily assemble an all-star crew.
Businesses are moving fast but still falling behind
While criminals are getting smarter and more effective, too many businesses are going in the other direction. It's probably a combination of wishful thinking and sustained weariness, but it's putting a lot at risk.
Size and industry are no longer a defense
While the headlines are filled with stories about the cybersecurity failures of large, well-known companies, threat actors are always looking far and wide for their next target. As large companies get more sophisticated about the way they protect critical assets, it's only natural that threat actors seek smaller, easier prey.
The move to a software-defined enterprise also makes smaller businesses more attractive. In many cases they're using the same applications and infrastructure as larger organizations, but without the same security maturity. Even moving to a public cloud still leaves much of the challenge in the laps of internal IT and security teams.
Data is a big asset, but a bigger liability
From sales operations and finance through to customer service, chances are you rely on data to either drive your business, or at least make it run faster and further. You're probably also collecting as much customer data as you can ethically get your hands on, while trying to stay compliant with the tougher and tougher rules where you operate.
Threat actors have also noticed you're increasing reliance on data, thus the rise of ransomware. But it's also great for just adding to the stress and strain of IT and security teams. In fact, compliance rules, many data-driven, put an average 4300 hours of work on the plates of IT and security teams at growing businesses.
Finally, third party risk is multiplying your obligations
Modern business relationships are increasing your attack surface just as regulators are becoming intensely focused on third party risk. You're now accountable for the security posture of partners. And you don't have to fall under security rules directly—business agreements will inevitably bring these rules your way.
The complexity of the software-defined business also makes this worse. Larger orgs have an average SaaS portfolio of 371 applications and services. Understanding and assessing 3rd party readiness, and being able to attest to your own, demands consistent standards for measuring and benchmarking. Those standards remain as big a barrier as any killer security app.
Where the data actually stands
If you stare long enough at cybersecurity headlines, it's easy to quickly get very discouraged – the hits just keep coming. Even as cybersecurity defenses get stronger, attackers manage to remain forever just out of reach. Businesses are struggling to acquire both talent and tech.
The latest numbers from IBM's Cost of a Data Breach Report 2026 are a reminder that progress isn't guaranteed. The global average cost of a breach climbed to $4.99 million, up 12% year over year; in the U.S. it reached $11.5 million. And for the first time in five years, the average time to identify and contain a breach increased, up 2.5% from 2025.
- One in four malicious breaches in the 2026 report were AI-enabled, a 56% increase year over year, averaging roughly $6 million per breach.
- Phishing, including voice and SMS phishing, remained the single most common way in, at 17% of breaches and $5.9 million per incident.
Taken together, the numbers say the opposite of "it's getting easier": attackers are moving faster and using better tools, and defenses built around a single checkpoint or one more point solution are falling further behind, not catching up.
How it's getting better: rethinking basics, reframing fundamentals
Security tools are getting smarter, but the shift in mindset is even more significant. Security in motion must be about orchestration beyond implementation. The same point solutions that once sat in a stack must become part of a connected whole that understands more and can respond more effectively.
Time to think in layers, not single checkpoints
Protecting the business from that professional heist crew was mostly about a good lock on the door (assuming they weren't planning a tunnel). The rise of zero trust has come from the failure of this paradigm: no single defense is sufficient, and you can't plan on catching the bad guys on their way in.
Beyond checkpoints and perimeters, it's time to view (and yield) controls in a layered approach. MFA is not "the answer" for identity—it's a single tactic that can be applied across the layer. Smart security strategies can analyze where MFA is way too much and where it's not nearly enough—and adjust accordingly.
Over time, these answers can be built into proactive strategies for better protecting data, identity, access, applications, and the other layers of your digital security.
Unlock intelligence through convergence
Getting smarter starts with quickly learning everything possible about the incident, evaluating risk, and responding with the right countermeasures. All those point defenses, less than effective on their own, suddenly take on new capabilities. These dynamic defenses, curated by human experts made smarter by AI, are the only possible answer to threats that are always being tested and sharpened.
It starts with smarter parts that make the whole more effective. As understanding context and circumstance becomes more critical to threat detection, businesses must connect the security and business systems required to unlock these answers. Each control can also become a sensor, and teams learn more about users, environments, and applications as a result.
Convergence works both ways. Each layer is an input to the whole, and lessons learned across the ecosystem help inform and align security components inside a meaningful strategy.
Complexity isn't going anywhere, but confidence is still possible
The continued gloom and doom around risk and cybersecurity is inevitable and understandable. For all our spending and innovation, the numbers always seem to move in the wrong direction. So where does the pivot begin? How can you be prepared for when the next heist crew, no matter how big or experienced, comes calling?
Proximia knows your best chance at cybersecurity success lies in giving your security experts the power of new solutions – and the ability to craft new strategies around them. This is how traditional controls and point defenses take on new effectiveness, while the best of what's next becomes part of the next generation of security and risk best practices.