Passwordless authentication replaces user-managed passwords with cryptographic credentials bound to a device or a biometric. It works well on modern systems. Most organizations, though, run hybrid environments that still include legacy platforms, VPNs, and remote desktop sessions that cannot support modern protocols. Fallback credentials survive in those gaps, which is why protecting the session matters more than reaching full passwordless coverage.
Key points
- Hybrid environments keep fallback credentials alive, because business systems cannot all modernize at once.
- Credential abuse still appears somewhere in the attack chain of 39 percent of all breaches (Verizon 2026 DBIR).
- The same report documents an authentication bypass pattern, where attackers steal session tokens to walk past MFA entirely.
- Session protection does not depend on every application supporting a modern protocol, which is why it closes the gap that passwordless coverage leaves open.
Why passwordless stalls in real environments
Passwordless deployments stall on inventory, not on ambition. The standards are mature and the modern half of the estate adopts them without much difficulty. The other half is where projects stop.
A typical environment runs a mix of cloud services, on-site platforms, VPN concentrators, remote desktop sessions, and line-of-business systems that predate the standards entirely. Some of those systems cannot support modern protocols at all. Others technically can, but sit behind a vendor release cycle, a compliance freeze, or a contract that makes changing them a multi-year project.
So passwords do not disappear. They retreat into the systems nobody can touch yet, and they stay there. That is not a failure of the security team. It is what happens when authentication modernization moves faster than the estate underneath it.
The fallback credential is the whole problem
A single surviving fallback credential undoes most of the benefit of a passwordless rollout. An attacker does not need to defeat the modern path when an older one still accepts a password.
This is measurable. More than 97 percent of identity attacks are password attacks, driven by large-scale guessing and spraying with credentials taken from leaks and infostealer malware (Microsoft Digital Defense Report 2025). And while credential abuse recently dropped to 13 percent of breaches as the initial way in, that figure understates the problem badly.
Credential abuse still appears somewhere in the attack chain of 39 percent of all breaches (Verizon 2026 Data Breach Investigations Report).
Read those two numbers together and the pattern is clear. Attackers increasingly get in through a vulnerability, then pivot to credential harvesting to move sideways and escalate. Credentials are no longer mainly the front door. They are the connective tissue of the attack once it is inside, which is exactly the role a fallback credential is best suited to play.
What “true passwordless” actually means
Most platforms marketed as passwordless still keep a password somewhere the user can reach. The user may not type it often, but it exists, they manage it, and they can fall back to it. That is a better experience, not a smaller attack surface.
The distinction worth holding onto is whether a user-known password exists at all. With Proximia®, no user-known password exists, ever. Where legacy systems such as Windows login, RDP, VDI, and LDAP still require password-format credentials, the platform generates them automatically. Users never create, see, know, or manage them, and they cannot be extracted.
That is a precise claim rather than a sweeping one. Password-format credentials still exist at the protocol layer, because those systems require them. What is removed is the part an attacker can phish and a user can reuse.
Why the session, not the sign-in, is the exposed surface
Here is the shift that matters, and it is the reason full passwordless coverage is the wrong finish line. Every credential-based control, passwordless included, protects one moment: the sign-in event. Nothing in that model confirms who holds the session afterward.
Attackers have adapted to exactly that. The 2026 DBIR documents an authentication bypass pattern in which attackers steal session tokens and OAuth credentials to walk past MFA entirely, naming CitrixBleed 2, device code phishing against Microsoft 365, and compromised Salesloft Drift OAuth tokens among the 2025 examples. None of those attacks needed to beat the authentication step. They took what the authentication step handed out.
The same gap opens physically. A signed-in workstation left unattended on a clinical floor, at a court clerk’s counter, or in a control room is an authenticated session in someone else’s hands, and no sign-in method prevents that.
Traditional systems verify identity once and then assume the session stays in the right hands until sign-out or timeout. That assumption creates three exploitable gaps: no session continuity, no presence awareness, and a persistent attack surface wherever credentials still exist.
What to do while your estate catches up
Protect the session, and the coverage problem stops being a blocker. Session-level protection does not ask whether an application supports a modern protocol, which is why it works across a hybrid environment rather than only across the modern part of it.
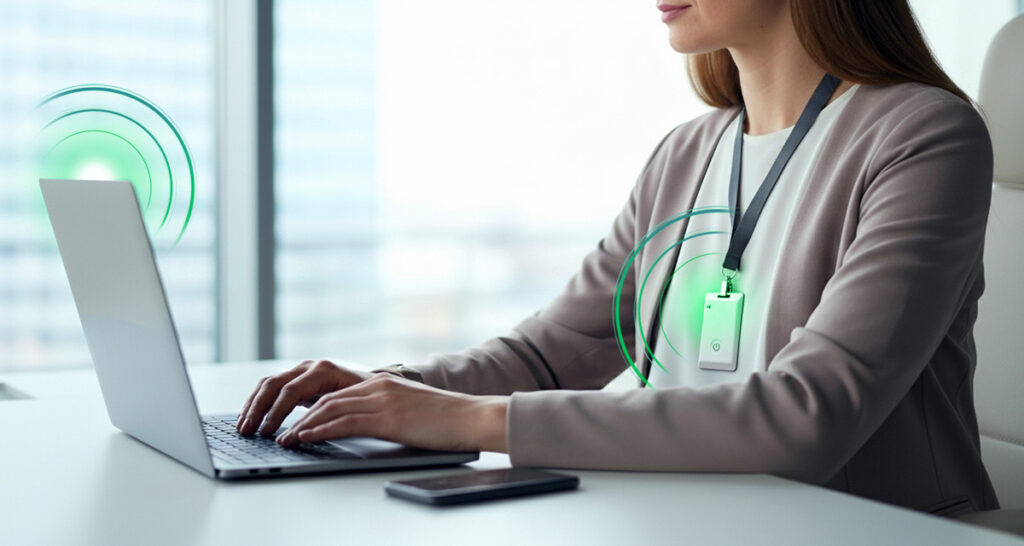
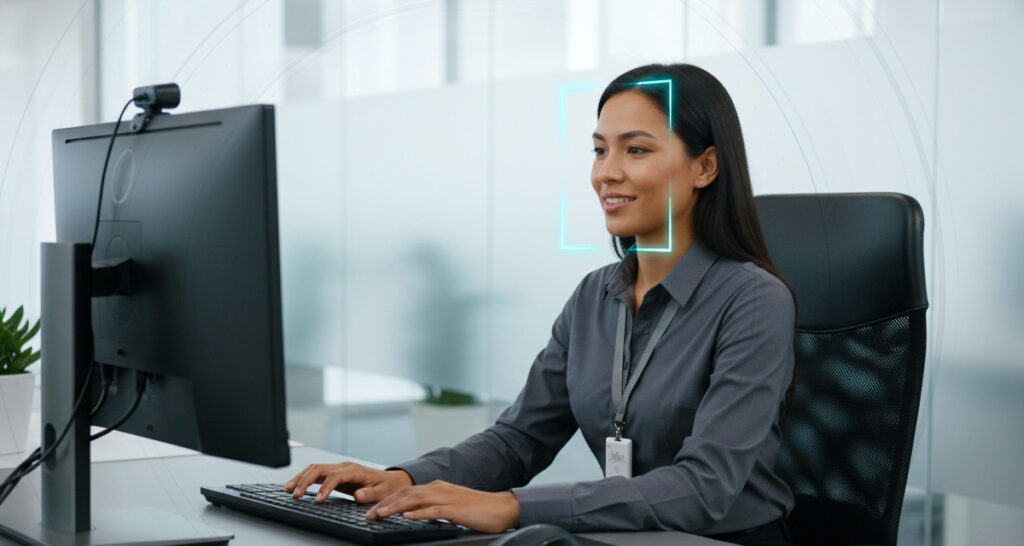
Proximia is a persistent, presence-aware authentication platform. A user signs in with live biometrics in about two seconds, with matching performed locally and raw biometric images never stored or transmitted. The XiFi® Card or the user’s phone then maintains an encrypted, mutually authenticated proximity check for the length of the session. When the user leaves the configured proximity zone, the session locks within seconds, and returning requires their biometric again.
Two properties make this practical during a long modernization. It integrates with Active Directory and Entra ID rather than replacing them, so it does not compete with the passwordless work already underway. And it applies the same session protection to systems that will never support a modern protocol, which is the half of the estate that has been holding the project up.
Walk up, work. Walk away, lock. Keep modernizing the systems that can be modernized. Stop treating full passwordless coverage as the point at which the environment becomes secure, because the session was always the exposed part. For a deeper comparison of platform options, see our guide to choosing the right authentication platform, or the difference between continuous authentication and a static sign-in.
Frequently Asked Questions
What does passwordless authentication actually mean?
Passwordless authentication replaces a user-managed password with a cryptographic credential bound to a device or a biometric. The important question is whether a user-known password still exists somewhere as a fallback. Many platforms marketed as passwordless keep one, which means the credential attack surface is reduced rather than removed.
Can an organization be fully passwordless today?
Rarely, and not quickly. Most environments include legacy platforms, VPNs, and remote desktop sessions that cannot support modern protocols, or that sit behind vendor release cycles and compliance freezes. Those systems keep fallback credentials alive, which is why session-level protection matters more than chasing complete coverage.
We already have MFA. Is that not enough?
MFA protects the sign-in event and does nothing to protect the session that follows it. The Verizon 2026 DBIR documents attackers stealing session tokens and OAuth credentials to bypass MFA entirely, without defeating the authentication step. Proximia protects the whole session and eliminates the credential, so there is nothing left to phish.
Does this require replacing our existing identity platform?
No. Proximia integrates with Active Directory and Entra ID rather than replacing them, using a lightweight agent. It is SOC 2 Type II certified and HIPAA aligned, and it supports FIDO2 and WebAuthn.
What happens to a session when the user walks away?
The session locks within seconds of the user leaving the administrator-configured proximity zone, which is typically five to thirty feet. Returning requires the user’s biometric again. Proximity alone never grants access; it is always combined with biometric identity and mutual device authentication.
Close the gap passwordless leaves open
Passwordless coverage will keep improving, and the systems holding it up will keep taking longer than anyone wants. The session is exposed either way, and that is the part you can protect now.
See how it works at proximia.com/how-it-works, or schedule a demo at proximia.com/contact.